
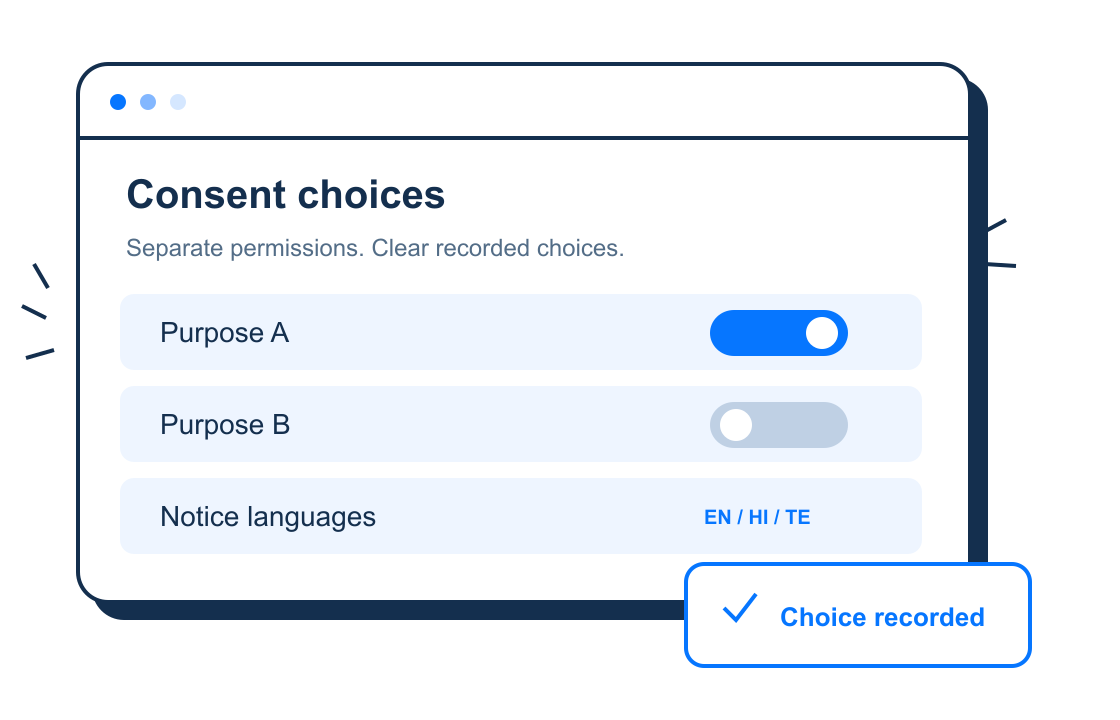
Consent management
Publish clear notices, record independent choices and manage purpose-specific withdrawals.
Consent management, privacy-rights workflows and runtime data governance for your DPDP, GDPR and EU AI Act programs. Protect sensitive data on connected routes with access controls and audit evidence.
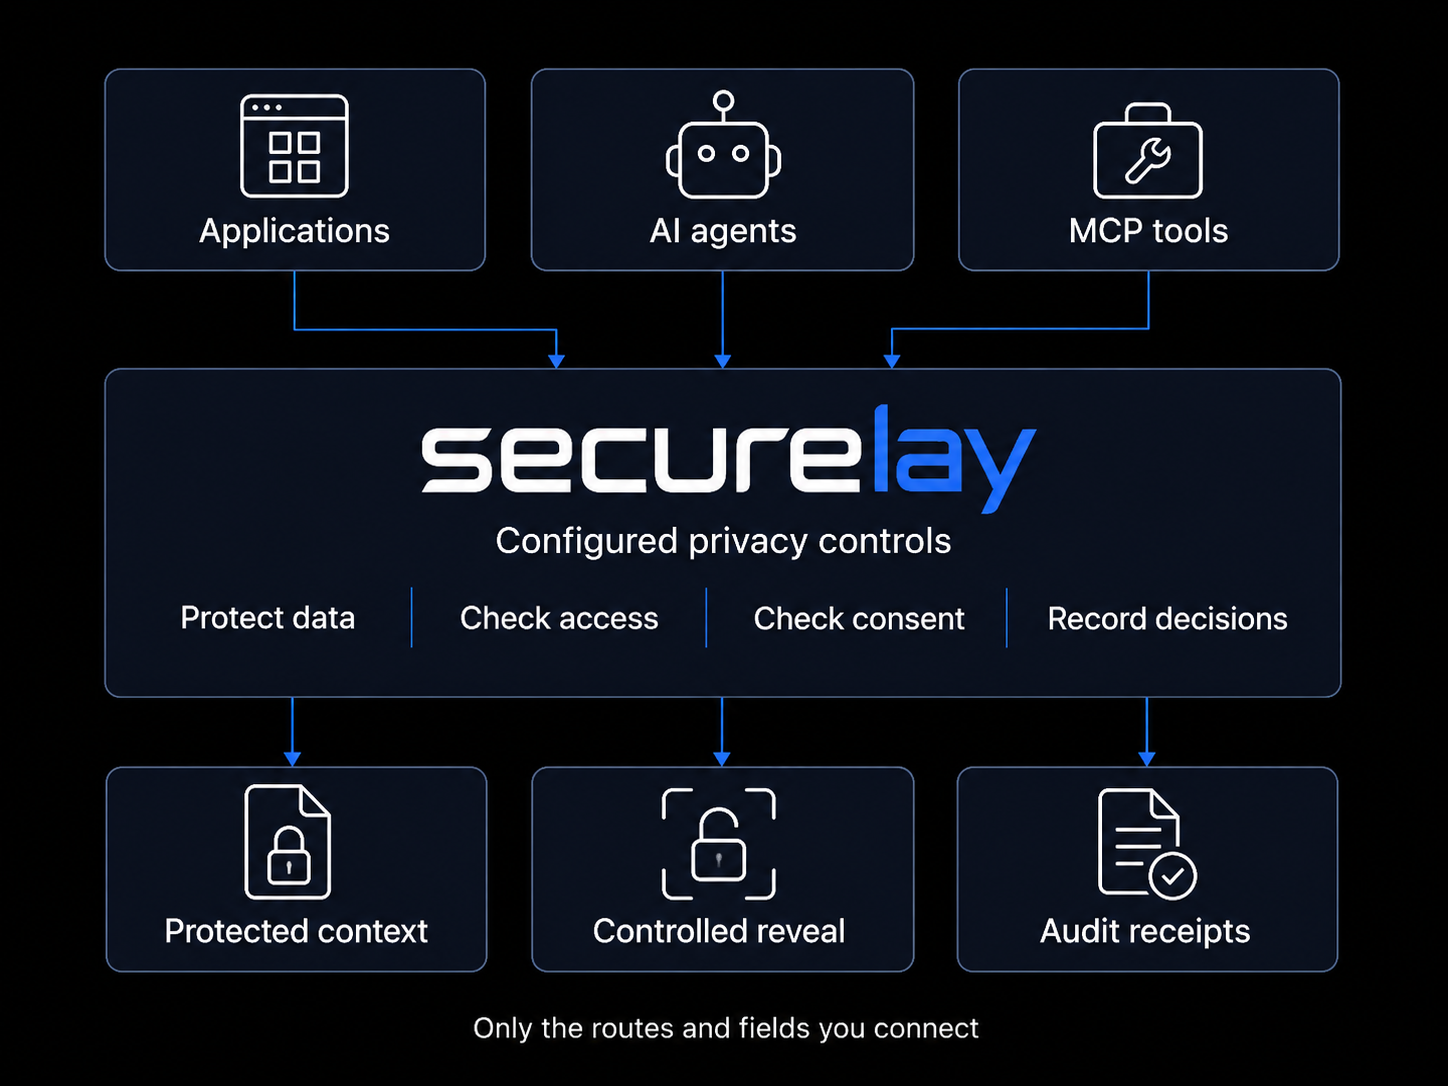
Consent management and a combined governance and vault offering, with DPO support around the workflows in scope.
Publish clear notices, record independent choices and manage purpose-specific withdrawals.
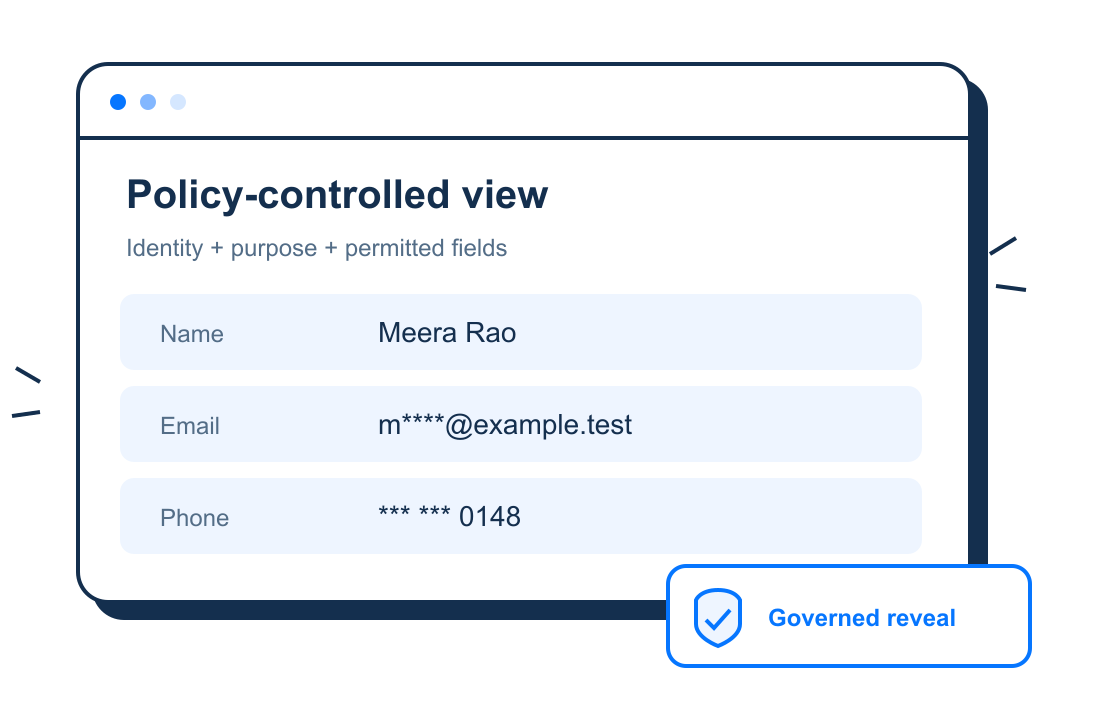
Replace selected values with tokens. Keep originals encrypted and reveal only what policy permits.
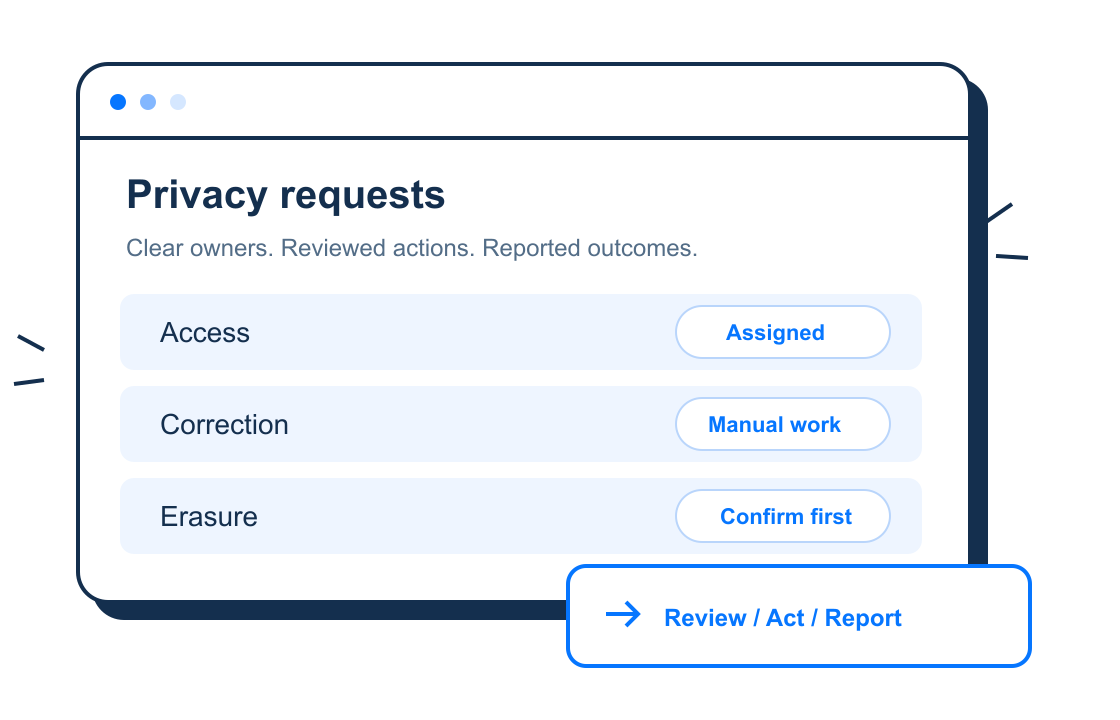
Give requests, retention and incident follow-up a clear owner. Review records and reported outcomes.
Publish clear notices, record independent permissions and connect privacy work to your own software. Keep sensitive values behind configured access checks.
How consent works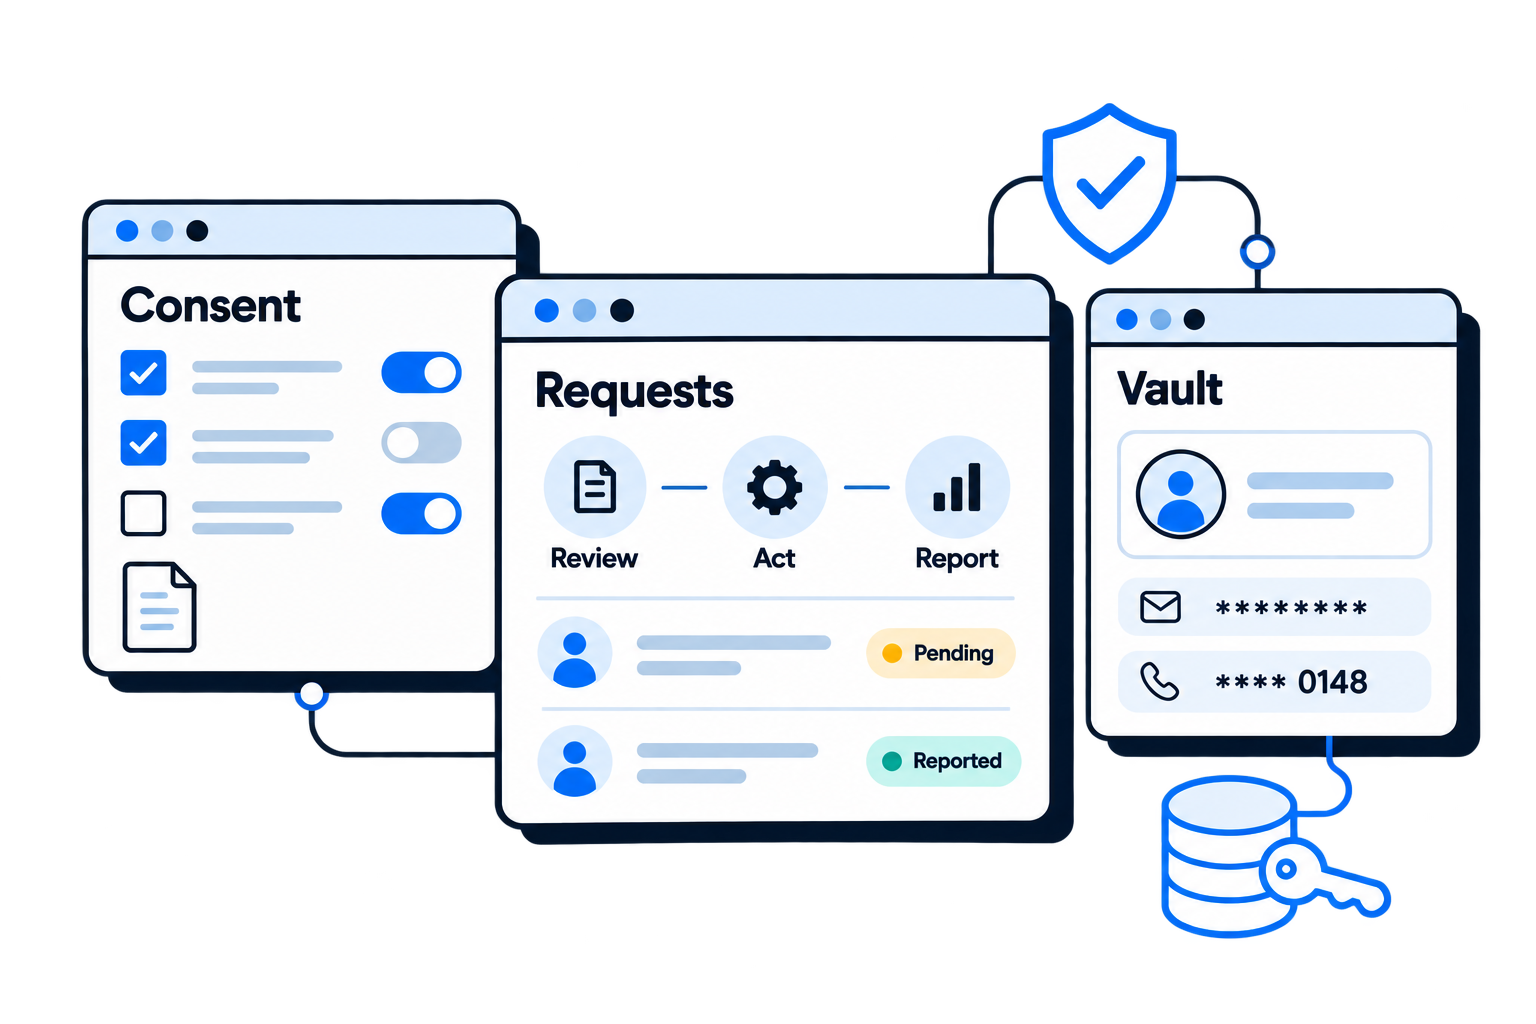
Your app keeps its branding and business data. Securelay records choices and coordinates the work you connect.
Assign access, correction, erasure, nomination and grievance requests.
Set rules, dates, recipients and reminders for follow-up work.
Maintain a versioned register of purposes, systems and responsible owners.
Record incidents, timelines, reviewed communications and report references.
See recorded activity, due work and evidence gaps, not a compliance score.
Separate staff activity, consent history and client-reported outcomes.
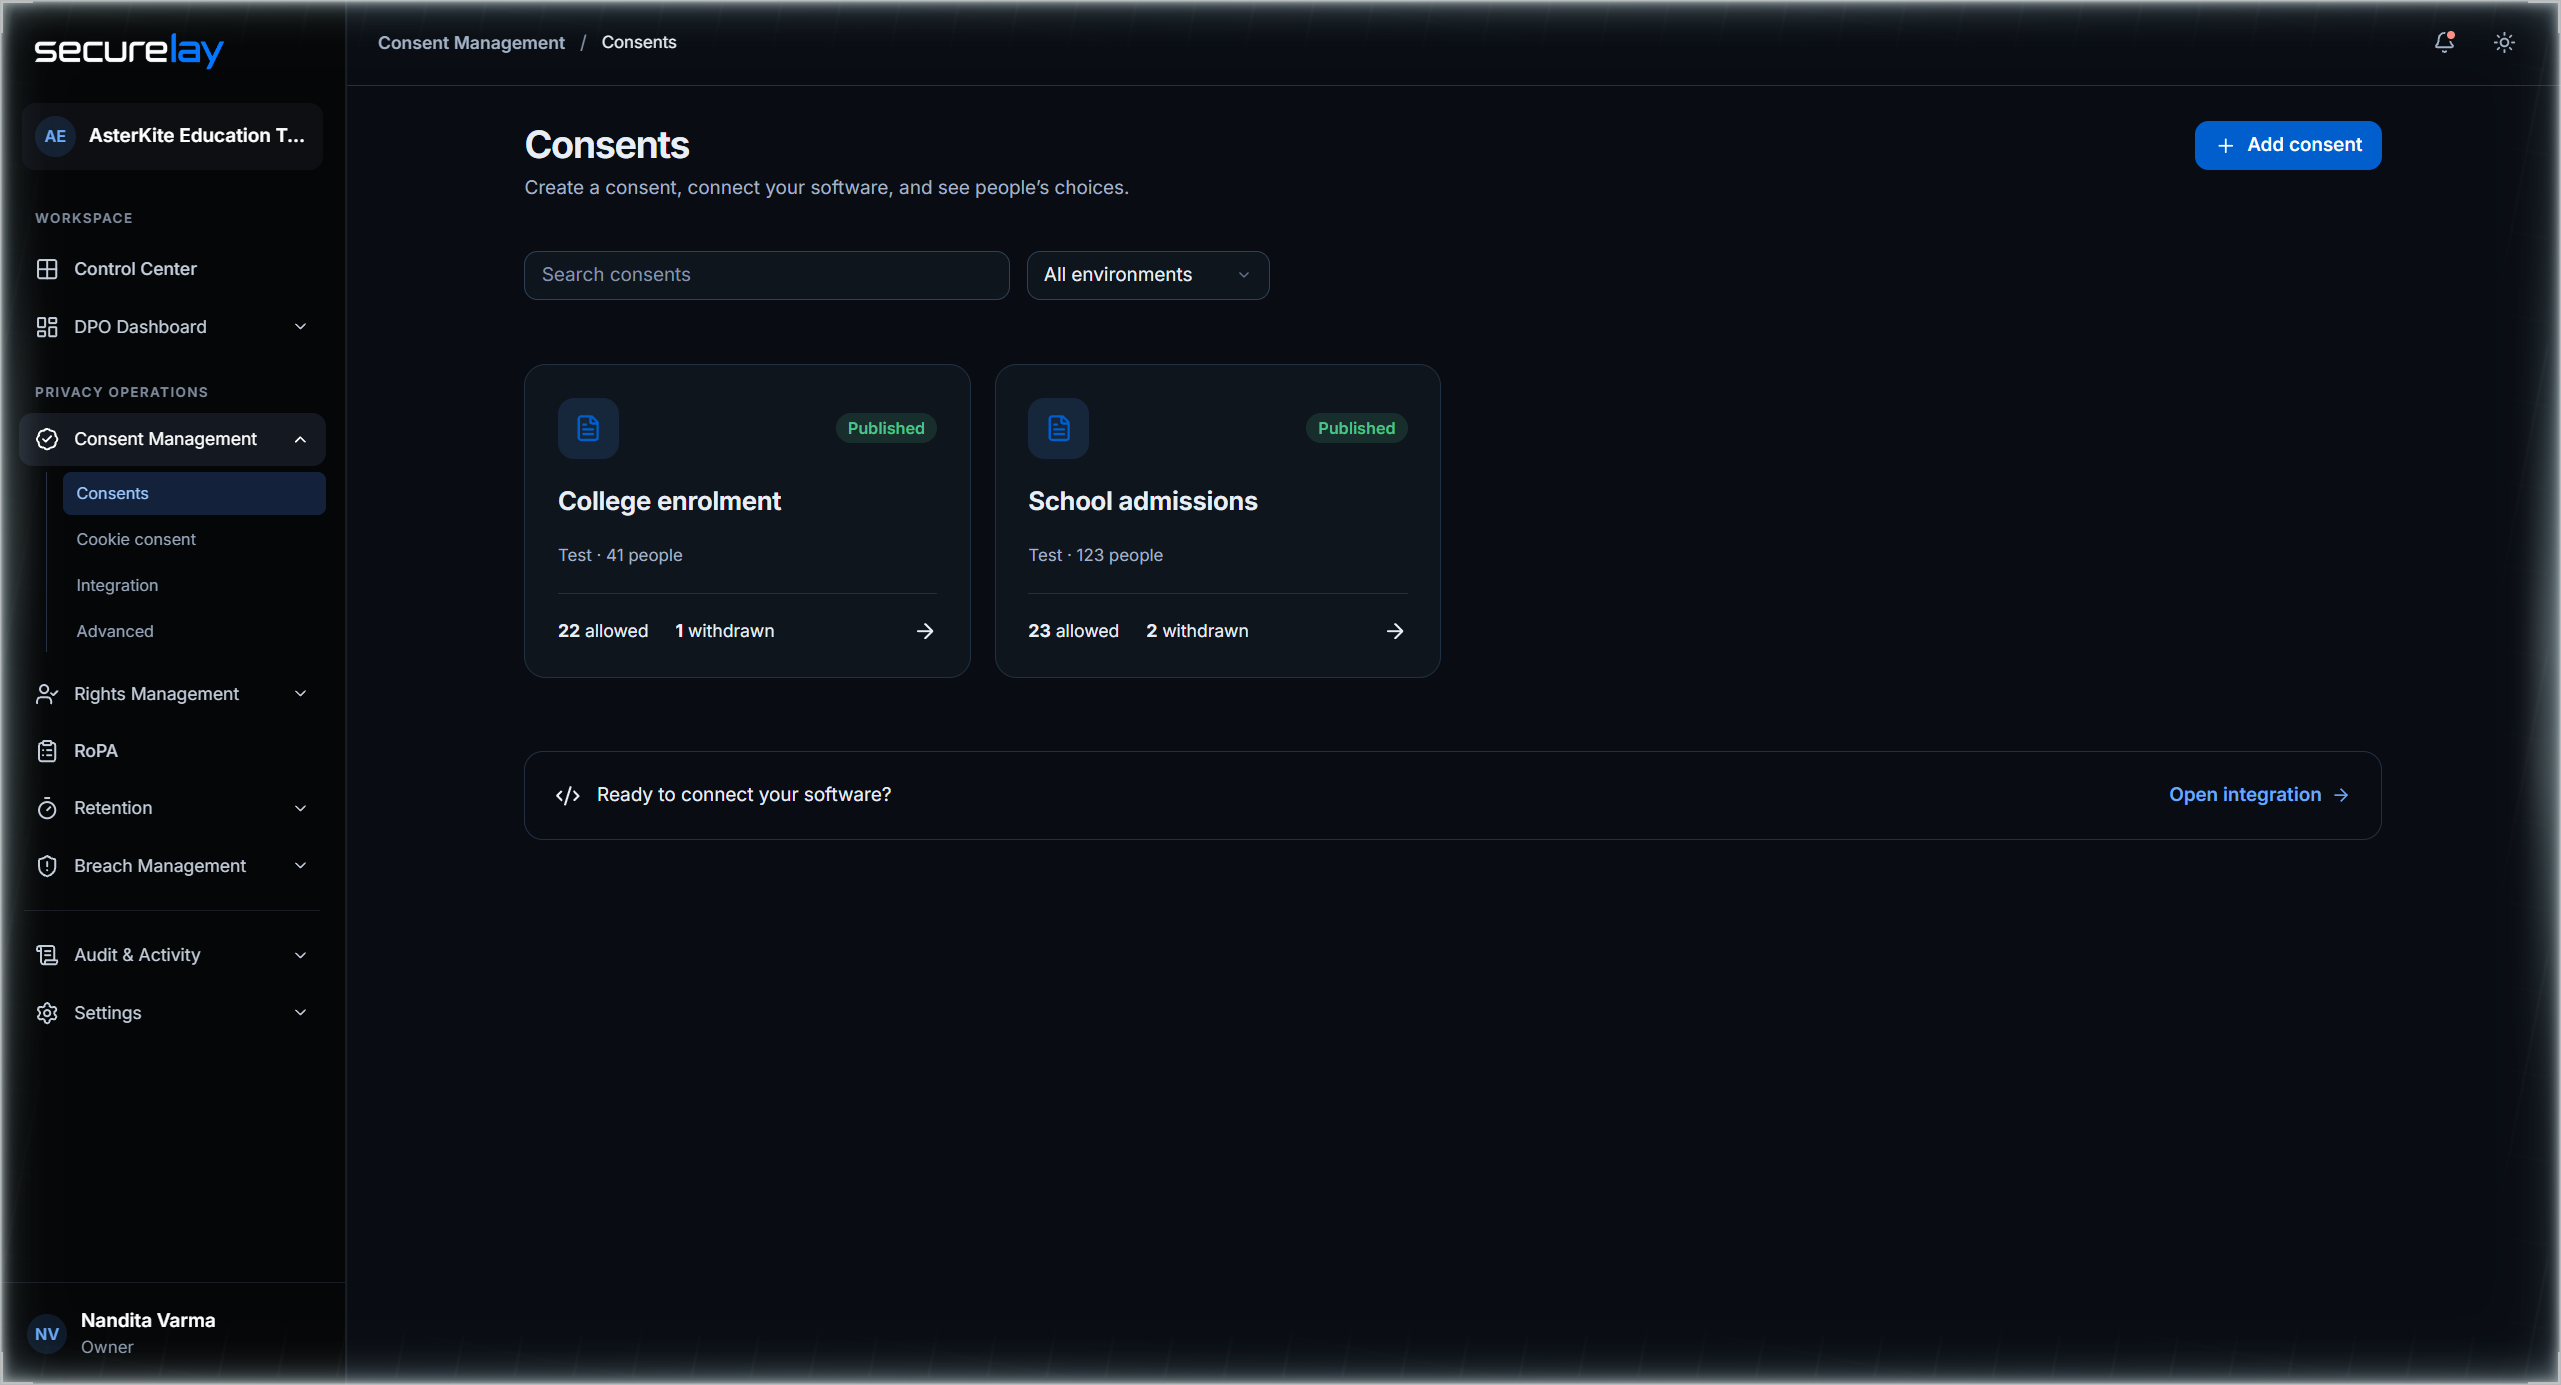
Client software checks consent before processing and reports its result. A delivered webhook is not completed work. Correction stays manual; erasure requires confirmation.
Use AI to work with documents while protecting selected personal details. Compare both views below.
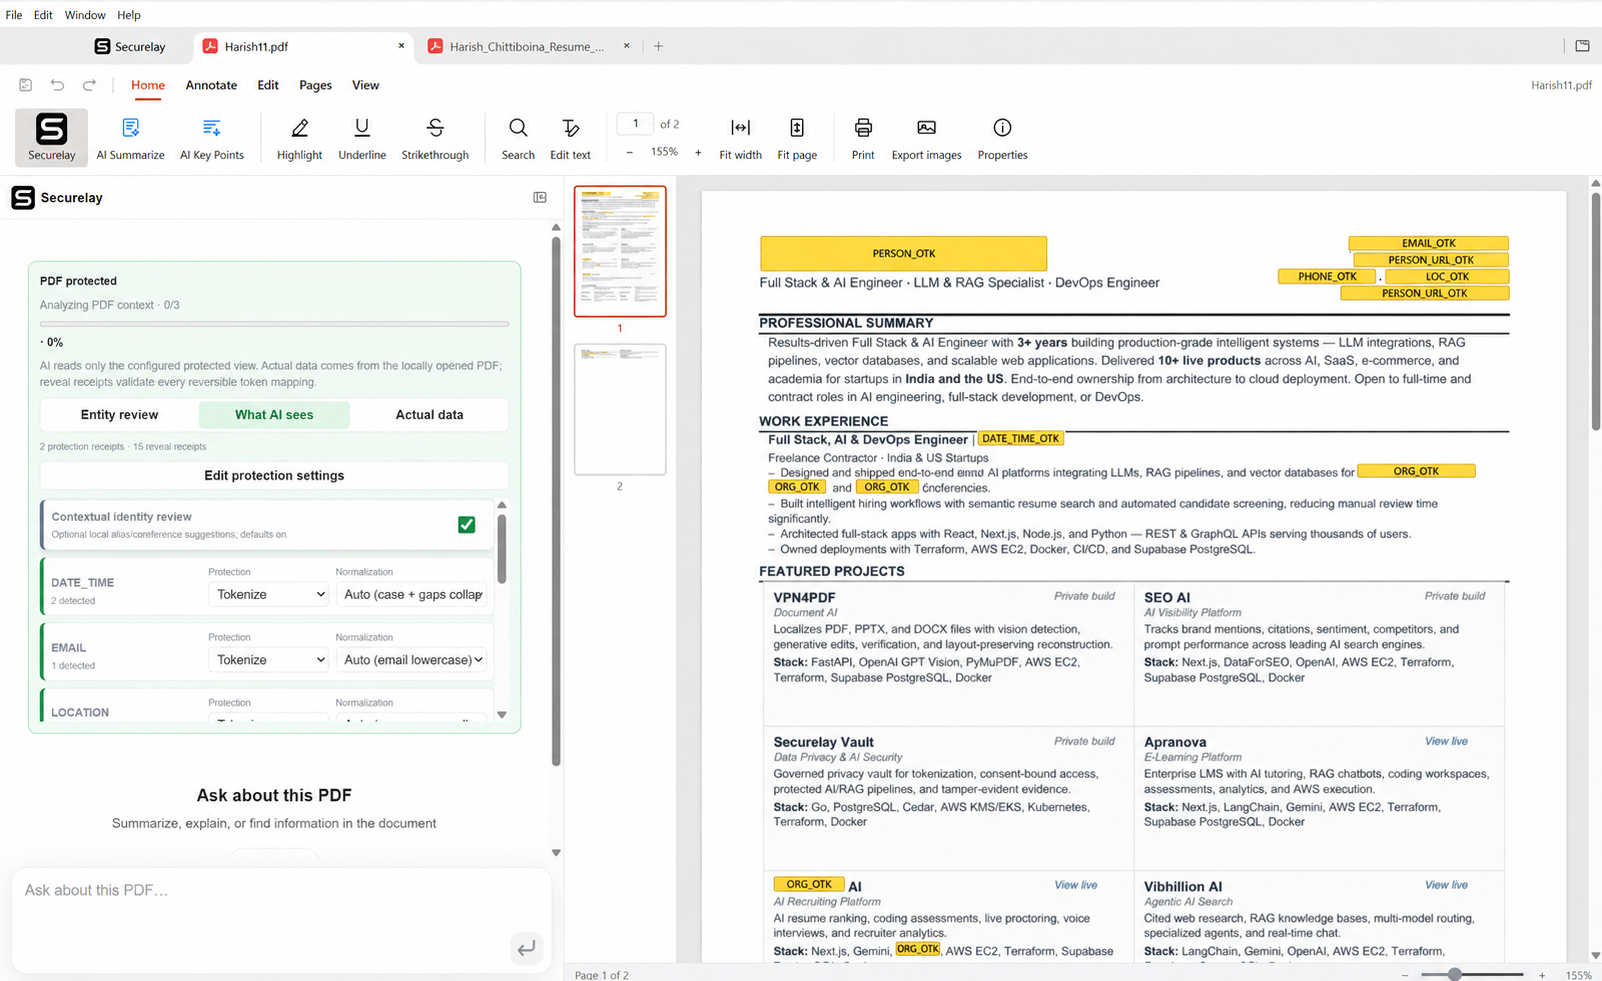
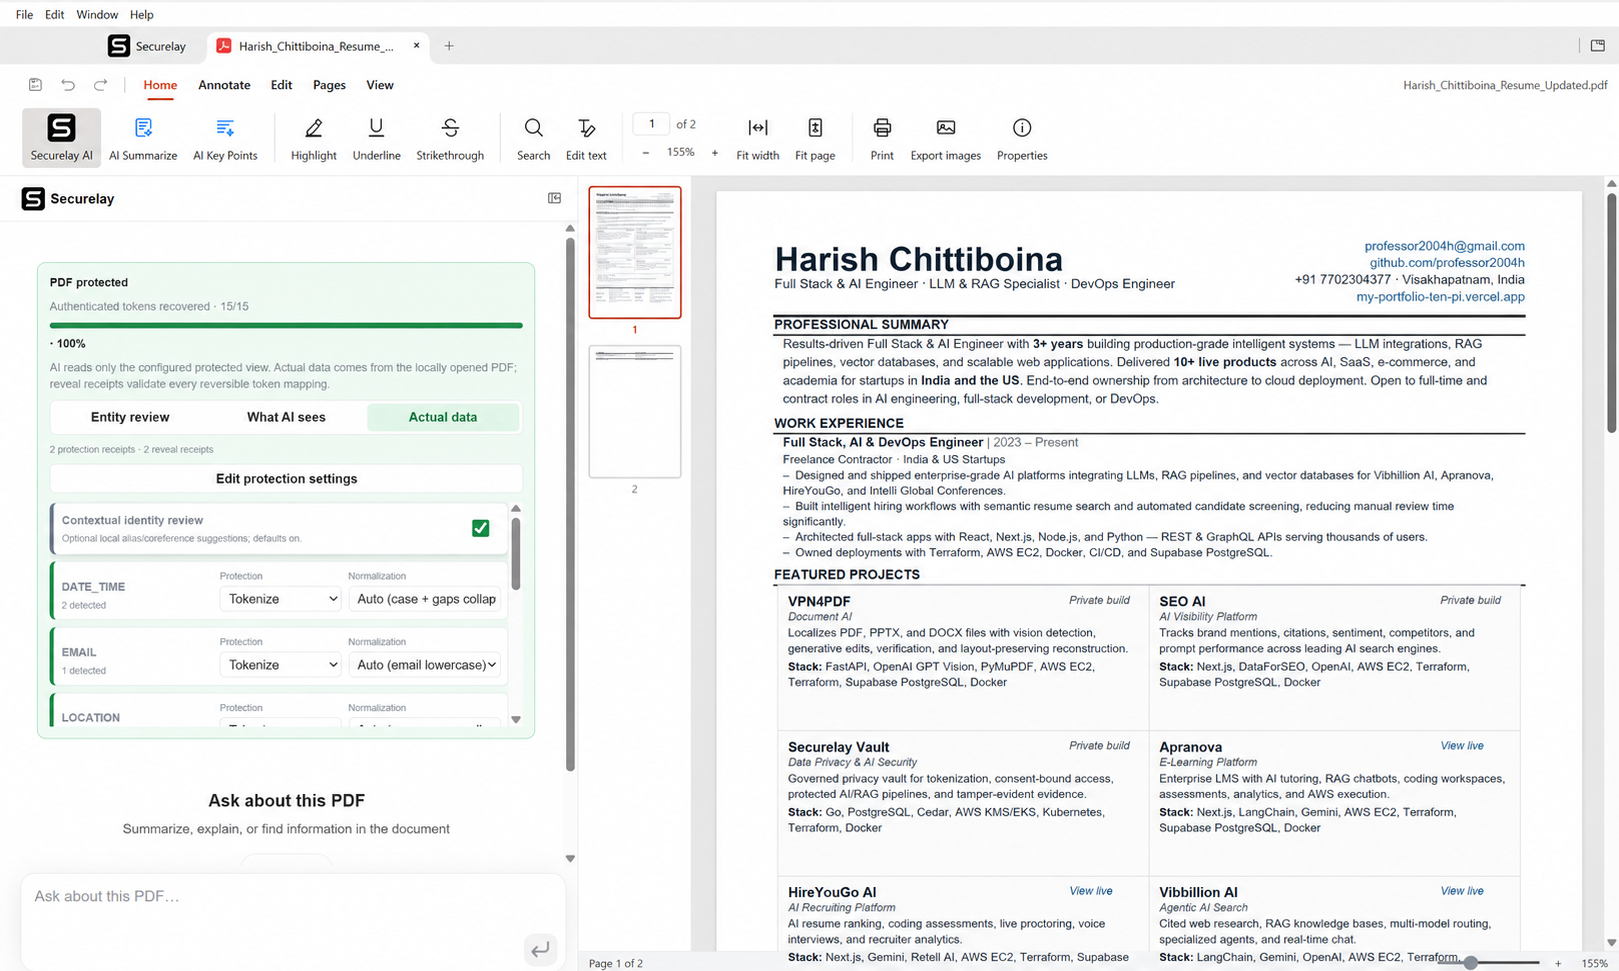
Three real views from one synthetic customer path: source plaintext, application tokens, and sealed Securelay custody.
 Open full image
Personal details appear in the original record.
 Open full image
Selected fields become tokens. The application keeps its customer record.
 Open full image
The protected values are held separately, encrypted by field.
What these screenshots prove. Protection applies to the fields and routes you connect. Tokenization reduces exposure; it does not make every copy or remaining field anonymous.


Swipe to explore the guides
Independent analysis, grounded in primary sources. Official imagery is editorial, not an endorsement.
Harish on LinkedIn